This guide provides comprehensive coverage of security best practices for cloud and container environments. Implementing these controls helps protect your infrastructure from threats while maintaining operational efficiency. Modern security requires a proactive approach that integrates security into every aspect of your infrastructure and development processes. This guide covers practical implementation …
 Editorial team
AWS Organizations Security: Multi-Account Strategy
This guide provides comprehensive coverage of security best practices for cloud and container environments. Implementing these controls helps protect your infrastructure from threats while maintaining operational efficiency. Modern security requires a proactive approach that integrates security into every aspect of your infrastructure and development processes. This guide covers practical implementation …
Kubernetes Admission Controllers: Policy Enforcement
This guide provides comprehensive coverage of security best practices for cloud and container environments. Implementing these controls helps protect your infrastructure from threats while maintaining operational efficiency. Modern security requires a proactive approach that integrates security into every aspect of your infrastructure and development processes. This guide covers practical implementation …
Kubernetes RBAC Deep Dive: Fine-Grained Access Control
Security is paramount in modern cloud environments. This comprehensive guide covers essential security practices, configurations, and implementation strategies for protecting your infrastructure and applications from threats. Understanding security fundamentals and implementing proper controls is essential for any production deployment. This guide provides practical examples and best practices that you can …
Kubernetes Network Policies: Complete Guide to Pod-Level Security
Kubernetes Network Policies provide a powerful mechanism for controlling traffic flow between pods, namespaces, and external endpoints. By default, Kubernetes allows all pod-to-pod communication, which creates significant security risks in multi-tenant environments. Network Policies enable you to implement micro-segmentation and zero-trust networking principles within your cluster. Understanding and implementing Network …
Policy as Code with Open Policy Agent (OPA)
Open Policy Agent (OPA) enables policy as code, allowing organizations to define and enforce policies across the stack using a declarative language called Rego. Rego Policy Example Gatekeeper in Kubernetes Conftest for CI/CD Policy as code ensures consistent enforcement across environments and provides version-controlled, auditable policy definitions. Related articles Secrets …
Secrets Management with HashiCorp Vault
HashiCorp Vault provides centralized secrets management, encryption as a service, and identity-based access. It eliminates hardcoded secrets and provides audit trails for all secret access. Vault Setup Kubernetes Integration Dynamic Secrets Dynamic secrets are generated on-demand and automatically revoked, eliminating long-lived credentials. Related articles Vault Transit Secrets Engine: Encryption as …
Software Supply Chain Security: SBOM and SLSA Implementation
Software supply chain attacks have increased dramatically, targeting dependencies, build systems, and distribution channels. Software Bill of Materials (SBOM) and Supply-chain Levels for Software Artifacts (SLSA) provide frameworks for securing the software supply chain. Supply Chain Attack Vectors Dependency Confusion: Malicious packages with internal names Typosquatting: Packages with similar names …
Edge Computing Security Challenges and Solutions in 2025
Edge computing brings computation closer to data sources, reducing latency and bandwidth usage. However, this distributed architecture introduces unique security challenges that require specialized approaches to protect edge devices and data. Edge Security Challenges Physical Security: Devices in uncontrolled environments Limited Resources: Constrained compute for security controls Network Exposure: Increased …
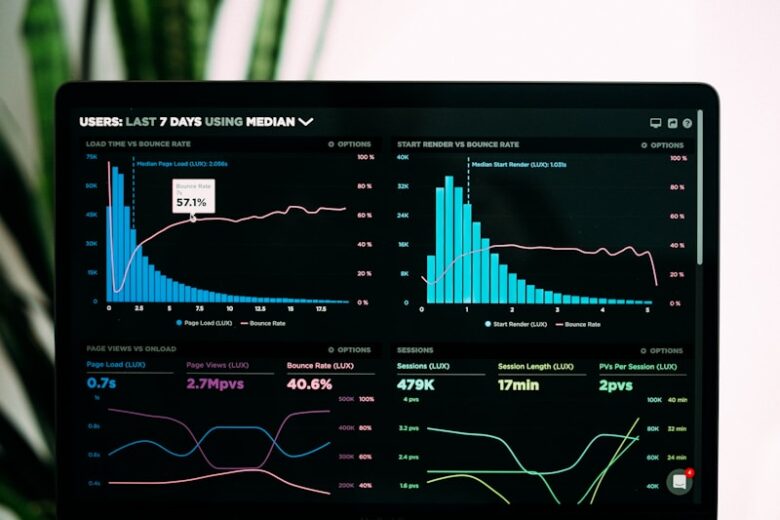
Infrastructure Observability and Distributed Tracing
Observability goes beyond traditional monitoring by providing deep insights into system behavior through metrics, logs, and traces. Distributed tracing is essential for understanding request flows across microservices architectures. Three Pillars of Observability Metrics: Numerical measurements over time (latency, error rates) Logs: Discrete events with context Traces: Request journey across services …
Service Mesh Security and Zero Trust Networking with Istio
Service meshes like Istio provide a dedicated infrastructure layer for handling service-to-service communication. They enable zero trust networking by implementing mutual TLS, fine-grained access control, and observability without changing application code. Zero Trust Principles in Service Mesh Never Trust, Always Verify: Authenticate every request Least Privilege Access: Explicit authorization policies …
Cloud Cost Optimization and FinOps Strategies for Engineerin
FinOps brings financial accountability to cloud spending by combining systems, best practices, and culture. This guide covers practical strategies for optimizing cloud costs while maintaining performance and reliability. FinOps Framework Phases Inform: Visibility into cloud spending and allocation Optimize: Identify and implement cost reduction opportunities Operate: Continuous governance and improvement …